
Artificial intelligence tools in enterprise software development have moved beyond the experimental stage, shifting the industry focus from isolated developer speed to the challenge of building sustainable, end-to-end delivery models at institutional scale.
Enterprise software development has crossed a decisive threshold. The early wave of curiosity, where organizations launched pilot programs and small-scale trials to test artificial intelligence capabilities, is rapidly giving way to a much more demanding operational phase. Across the global technology landscape, artificial intelligence assistants, code generators, and automated developer tools are no longer viewed as novel experiments confined to isolated sandboxes. They have entered daily development workflows, demonstrating clear capacity to accelerate specific coding tasks, streamline repetitive documentation, and assist engineers with routine logic generation.
Yet, as these tools establish a permanent foothold across engineering floors, enterprise leaders are confronting an unforeseen operational paradox. While individual programmers and isolated engineering squads report significant speed gains during initial drafting and coding phases, these localized efficiencies do not automatically translate into faster, safer, or more effective software releases at the organizational level. The fundamental question confronting modern enterprises is no longer whether automated coding tools can generate algorithms more quickly, but whether institutions can orchestrate these discrete gains across the entire software delivery lifecycle in a manner that remains reliable, secure, and sustainable at scale.
According to technology leaders overseeing major digital transformations, long-term competitive advantage will not belong simply to the companies that license the latest generative tools or encourage their engineers to write prompts. Instead, enduring market leadership will be determined by an organization’s capacity to govern, integrate, and scale these technologies within a coherent, institution-wide operating model.
Bridging the Gap Between Isolated Speed and Systemic Delivery
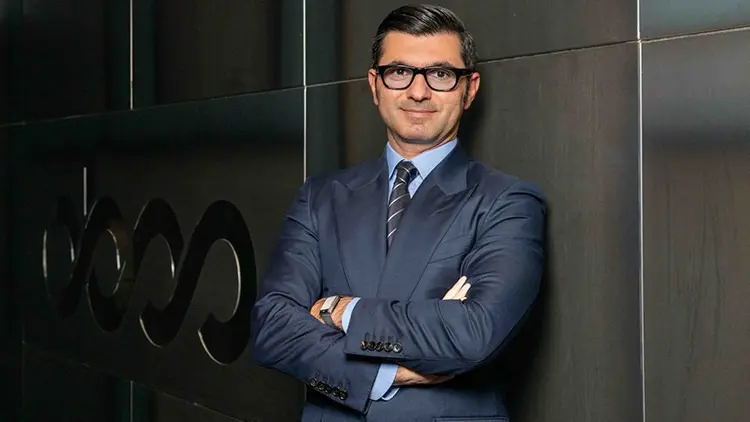
The transition from localized developer productivity to comprehensive enterprise value forms the central theme of recent assessments by Zafer Şen, Founder and Chief Executive Officer of OBSS, an international software solutions and engineering consultancy. Addressing the evolving role of artificial intelligence within complex technical ecosystems, Şen underscores that turning isolated technical accelerations into genuine commercial and institutional value requires an end-to-end software delivery approach.
"Today, many organizations can develop faster with artificial intelligence," Şen observed in his evaluation of current industry trends. "However, in large-scale structures, the real issue is not speeding up a single step; it is carrying this gain across the entire software delivery lifecycle. For this, a reliable and repeatable operating model is required where quality, security, risk management, and engineering standards are reconsidered together with artificial intelligence."
Şen’s assessment points directly to a systemic challenge facing modern enterprise architecture. In conventional software engineering, writing source code represents only one link in an extensive, interconnected chain. Before any unit of code reaches a production environment where it interacts with real users, financial accounts, or mission-critical systems, it must traverse multiple gatekeeping processes. These encompass architectural validation, rigorous peer review, comprehensive automated and manual testing, compliance verification, performance benchmarking, security vulnerability scanning, and complex release engineering.
When artificial intelligence sharply accelerates only the initial stage of code creation without corresponding adaptations across downstream verification phases, severe bottlenecks emerge. Testing pipelines become congested with higher volumes of generated code, security teams find themselves overwhelmed by the sheer velocity of incoming pull requests, and release managers struggle to maintain structural integrity across interdependent systems. Without an overarching delivery framework that re-engineers the entire progression from inception to deployment, accelerating code production risks merely transferring friction from one department to another, leaving total cycle times largely unchanged while multiplying operational risk.
The Hidden Hazards of Engineering Fragmentation
In large, multi-tiered corporate structures, the unregulated proliferation of artificial intelligence tools introduces serious operational vulnerabilities. In the absence of an overarching organizational strategy, individual business units, product groups, or regional development squads often adopt disparate platforms, third-party plugins, and localized prompting practices. This decentralized approach frequently fragments core development standards across the enterprise.
When different departments rely on divergent tools and uncoordinated workflows, institutional consistency begins to deteriorate. Development standards fracture as teams apply contrasting conventions and architectures. Security policies are implemented unevenly, creating blind spots where code generated by unvetted models might bypass internal data loss prevention protocols or introduce subtle vulnerabilities into the broader codebase. Quality assurance mechanisms, calibrated for the cadence of human-written software, can struggle to identify edge cases, logic drifts, or subtle regressions hidden within syntactically correct, machine-generated scripts.
Furthermore, unmanaged adoption poses an acute risk to corporate institutional knowledge. Software development is fundamentally an exercise in collective institutional memory; it requires an engineering organization to understand not merely how a specific feature functions today, but why specific architectural decisions, trade-offs, and design patterns were adopted in the past. When machine-generated code is integrated without unified documentation standards, auditable lineage, and consistent architectural oversight, the enterprise risks losing ownership of its underlying technical knowledge. Over time, the inability to systematically manage and trace institutional knowledge diminishes maintainability, rendering future modifications, upgrades, and system migrations vastly more complex and hazardous.
Mission-Critical Environments and the Imperative for Governance
These architectural and managerial challenges become exceptionally severe in highly regulated and mission-critical industries. Sectors such as commercial banking, financial market infrastructure, defense systems, and aerospace engineering operate under uncompromising standards where software failures can precipitate financial contagion, national security threats, or direct risks to human life.
In these sensitive environments, adopting artificial intelligence cannot simply be treated as an exercise in developer convenience or raw output volume. As Şen emphasized, deploying artificial intelligence within critical and regulated technology domains requires a substantially more advanced engineering philosophy and a sophisticated governance apparatus.
"When redesigning the way we work with artificial intelligence in critical technology environments such as banking, defense, and aerospace, it is necessary to embed risk management, security, quality, and regulatory requirements into this new model from the very beginning," Şen stated. "For this reason, it is critical that the output generated is verifiable, decisions are traceable, and engineering accountability is preserved."
In banking and high-finance environments, software systems must continually satisfy stringent regulatory oversight regarding transaction security, data privacy, and systemic risk mitigation. Code that executes monetary transfers, manages customer portfolios, or calculates regulatory capital cannot simply appear functionally correct; its internal logic must be thoroughly explainable to internal compliance boards and external regulators alike. Similarly, in defense and aerospace applications, software systems run avionics, autonomous navigation, and secure communication channels where every operational parameter must conform to deterministic safety tolerances.
Embedding risk management and compliance directly into the software lifecycle ensures that automated outputs are continuously auditable. If an artificial intelligence tool assists in designing an algorithm, refactoring a legacy module, or generating an automated deployment script, the enterprise must maintain full traceability: identifying which inputs guided the model, what automated checks validated the result, and which human engineer validated the code’s fitness for purpose. Preserving unambiguous engineering accountability prevents the dangerous dilution of professional responsibility, ensuring that human oversight remains the definitive anchor for software reliability.

Redefining the Strategic Benchmark for Enterprise AI
As corporate leadership re-evaluates technological investments, the criteria used to measure digital maturity are undergoing a fundamental recalibration. In the early stages of generative technology adoption, executive scrutiny often centered on superficial adoption metrics, tracking how many developers had acquired licenses or how frequently digital assistants were engaged during coding sessions.
Today, forward-looking enterprises recognize that mere tool utilization does not correlate with enduring operational resilience or structural competitive advantage. The central strategic question for technology organizations has definitively shifted away from whether their teams are utilizing artificial intelligence tools. Instead, the defining inquiry for modern software leadership is how effectively the organization can convert artificial intelligence-assisted development into a dependable, scalable, and continuously improving operating model capable of delivering sustained value across the entire enterprise.